You do not need to build networks to audit them. You need to read one rule and know whether it is dangerous.
Addresses
Every system has an IP address.
- Private addresses, like
10.0.1.25, only work inside the company's network. - Public addresses, like
203.0.113.10, can be reached from the internet.
Ports
A port is a numbered door on a system, each for one kind of traffic:
| Port | What it is for | Open to the internet? |
|---|---|---|
| 443 | Websites (HTTPS) | Normal for a public website |
| 22 | SSH, admin login to servers | Should not be |
| 3389 | Remote desktop to Windows | Should not be |
| 5432 / 3306 | Databases (PostgreSQL / MySQL) | Never |
Firewall and security group rules
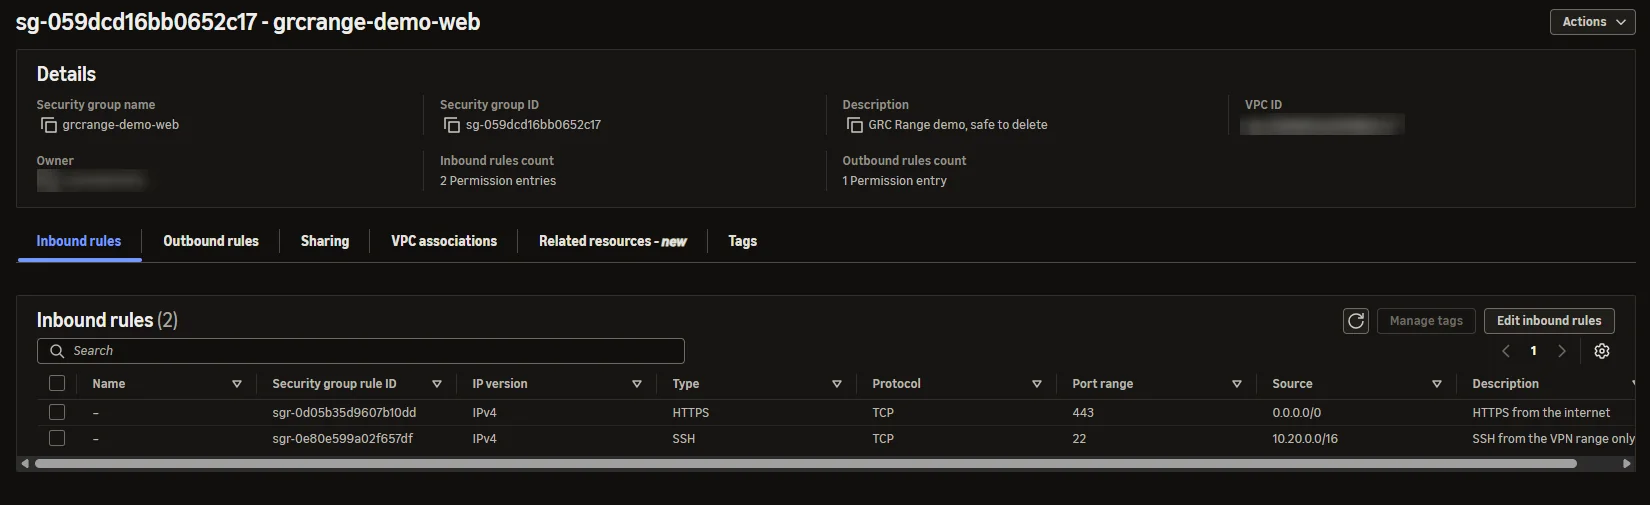
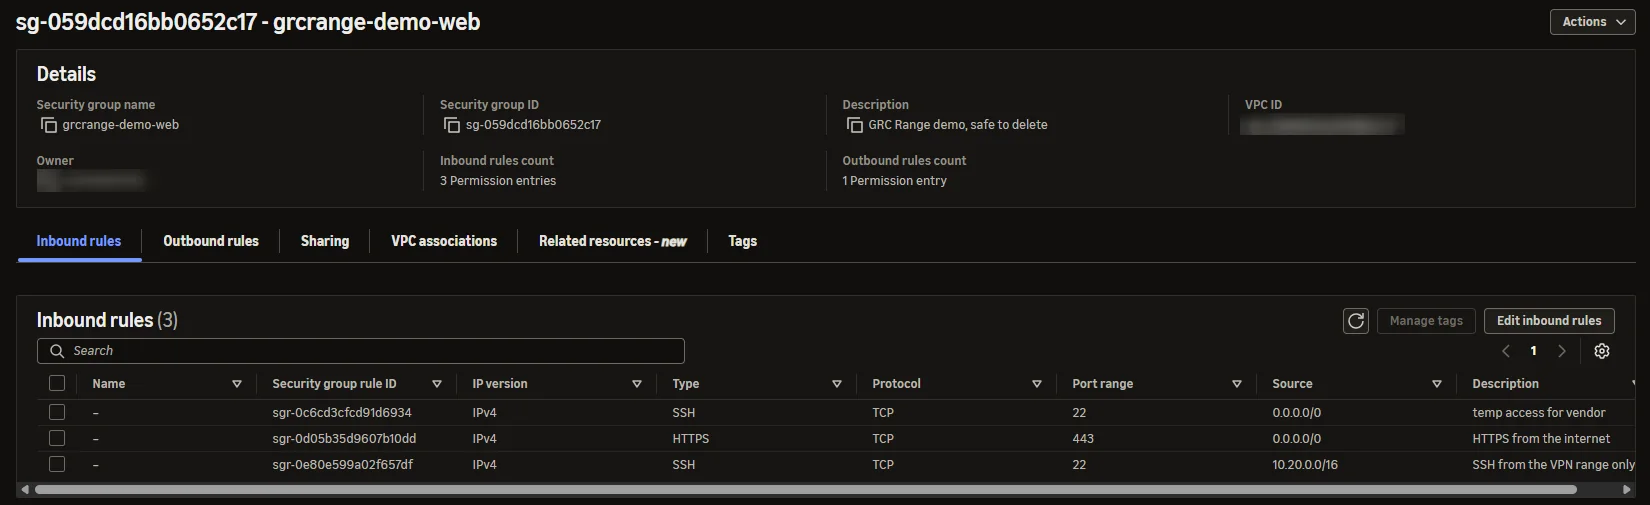
A firewall, called a security group in AWS and a network security group in Azure, is a list of rules. Each rule says: traffic from this source, to this port, is allowed.
The source 0.0.0.0/0 means any address on the internet. That is fine on port 443 for a website. On port 22 or a database port, it is one of the most common findings in cloud audits.
Other words you will meet
- VPC / virtual network: the company's private network in the cloud. Subnets divide it. Keeping production in its own network is called segmentation.
- VPN or zero-trust access: how staff reach internal systems from home, ideally with MFA.
- WAF: a web application firewall that filters attacks on websites.
What this means for evidence
For each production rule ask: what source, what port, and does the business need it? A screenshot of rules with a date and the account ID is the evidence. Any database or admin port open to 0.0.0.0/0 is an exception.
Inbound rules: db-prod
| Type | Port2 | Source3 | Description |
|---|---|---|---|
| PostgreSQL | 5432 | sg-07c2 (app-servers) | App servers only |
| PostgreSQL | 5432 | 10.0.8.0/24 (bastion subnet) | Admin access via bastion4 |
- 1Date, account and region. Network rules change, so the date matters.
- 2Port 5432 is PostgreSQL, a database. It should never face the internet.
- 3The source is another security group, not 0.0.0.0/0. Only the app servers can connect.
- 4Admin access only from the bastion subnet, a private 10.x range, with a description saying why.
Weak version: Port 5432 open to 0.0.0.0/0 means anyone on the internet can try to reach the database. This is an exception, not evidence of the control.
TLS configuration: api.complyoo.com
| Check | Result2 |
|---|---|
| Certificate | Valid until 2027-02-11, trusted issuer |
| TLS 1.2 and 1.3 | Enabled |
| TLS 1.0 and 1.1 | Disabled3 |
| HTTP to HTTPS redirect | Enforced |
- 1Scan date and the exact host scanned.
- 2Each check with its result, from the scanning tool rather than a claim.
- 3Old TLS versions disabled. Leaving them on is a common finding.
Weak version: A browser padlock screenshot shows a certificate exists. It says nothing about which TLS versions are allowed.
Source, port, allow. And 0.0.0.0/0 means everyone.
1. A security group allows 0.0.0.0/0 on port 5432. What does that mean?
2. Which of these is normal to open to the whole internet?
3. 10.0.1.25 is a...