Two different questions
- Authentication asks who are you? A password, plus a second factor.
- Authorisation asks what are you allowed to do? That comes from roles, groups and permissions.
A control can pass one and fail the other. Everyone may use MFA while half of them hold admin rights they do not need.
The pieces
- User: one person's account.
- Group: a set of users given the same access, such as "engineering".
- Role: a bundle of permissions, such as "read-only" or "administrator".
- Service account: an account used by software, not a person. Each needs a named owner.
- SSO (single sign-on): one login, through an identity provider such as Okta, Microsoft Entra ID or Google Workspace, that unlocks many apps. Turn a person off there and every connected app follows.
- MFA (multi-factor authentication): something you know (a password) plus something you have (a phone prompt or security key).
The accounts auditors look at first
- Root or global admin: can do anything, so it must have MFA and barely be used.
- Shared accounts: if five people use one login, nobody is accountable.
- Leavers and movers: accounts that should have been disabled or reduced.
What this means for evidence
Ask for the setting (MFA required for everyone) and the result (a report showing each user's MFA status). One without the other is half a proof.
Global session policy: Default rule
- Applies toEveryone2
- Multifactor authenticationRequired3
- Factors allowedOkta Verify (push), FIDO2 security key. SMS disabled4
- Session lifetime12 hours
- 1Date and Okta tenant.
- 2Applies to everyone, not a pilot group.
- 3MFA required, not optional.
- 4Weak factors such as SMS disabled. A strong extra point.
Weak version: MFA applies only to the IT group. Everyone else signs in with a password alone.
Credential report
| user | password_enabled | mfa_active2 | password_last_used | access_key_1_active |
|---|---|---|---|---|
| <root_account> | not_supported | true | 2026-02-11 | false3 |
| arjun.m | true | true | 2026-09-30 | false |
| david.e | true | true | 2026-09-30 | true |
| maria.s | true | true | 2026-09-29 | false |
| deploy-bot | false | n/a | n/a | true4 |
- 1Generated date and account ID. The auditor needs to know when and where this came from.
- 2mfa_active is the column that proves the control. It must be true for every user with a password.
- 3Root account has MFA. Auditors always check root separately.
- 4Service users have no password, so MFA does not apply. Their access keys are covered by key rotation instead.
Weak version: Cropped to three users, no date and no account ID. The auditor cannot tell when it was taken, which account it is, or whether anyone was left out.

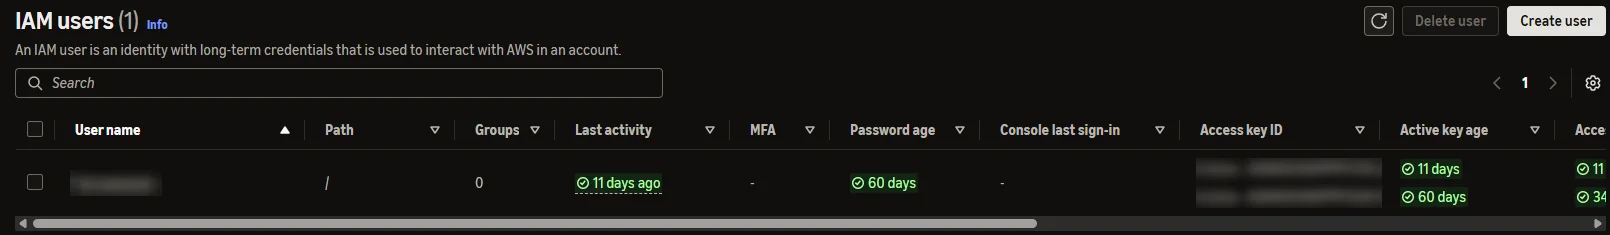
Access review results: Q3 2026 admin roles
| User | Role | Reviewer2 | Decision3 | Reason | Applied |
|---|---|---|---|---|---|
| arjun.m | Global Reader | vikram.k | Approve | On-call lead | Yes |
| neha.t | User Administrator | vikram.k | Deny | Moved to sales in August | Yes4 |
| david.e | Application Administrator | priya.r | Approve | Owns SSO integrations | Yes |
- 1Completion date inside the quarter.
- 2The reviewer is a manager who knows the work, not the person holding the role.
- 3Each line has a decision and a reason.
- 4A denial that was applied. A review with no removals at all invites questions.
Weak version: Everything approved by one person, no reasons, nothing removed. This looks like a signature, not a review.
Who are you, and what are you allowed to do? Two questions, two different controls.
1. "MFA required for all users" is evidence of...
2. Why does disabling someone in Okta matter so much?
3. Which account does an auditor usually check first?