The words
- Vulnerability: a weakness, such as outdated software with a known flaw, or a bad setting.
- CVE: the public ID given to a known vulnerability.
- CVSS: a severity score from 0 to 10. Policies set fix deadlines by severity, for example critical in 7 days and high in 30.
- Misconfiguration: a setting left unsafe, such as a public storage bucket. Cloud tools such as AWS Security Hub and Defender for Cloud flag these.
Scan vs penetration test
- A scan is automated, frequent and broad. It finds known problems.
- A penetration test is people trying to break in, usually yearly or before a major release. It finds what scanners miss, such as flaws in how an application works.
Companies need both, and auditors ask for both.
What this means for evidence
- Scan results for the period, with severity and dates.
- A ticket for each serious finding, with an owner.
- Fix dates compared with the policy's deadlines. Late criticals are exceptions.
- The penetration test report, plus proof the findings were fixed.
A dashboard showing a score is not enough. Auditors need the findings and what happened to each one.
Security Hub findings tracked to a ticketAWS Security Hub · proves CC7.1, A.8.8, A.8.9
AWS Security HubSAMPLE
Security Hub › Findings
Findings: severity Critical and High
| Severity | Title | Resource | Created | Workflow2 | Ticket3 |
|---|---|---|---|---|---|
| CRITICAL | Security group allows 0.0.0.0/0 on port 5432 | sg-0a91 (db-prod) | 2026-09-12 | RESOLVED | SEC-412 |
| HIGH | EC2 instance has a CVE score 8.8 package | i-07f2 (api-3) | 2026-09-20 | RESOLVED | SEC-418 |
| HIGH | IAM access key older than 90 days | deploy-bot | 2026-09-25 | NOTIFIED | SEC-4214 |
- 1Export date. Findings change daily, so the date matters.
- 2Workflow status shows each finding was handled, not just detected.
- 3A ticket for every finding links detection to remediation.
- 4Open finding still inside the policy's fix window. The auditor will check the deadline.
Weak version: A dashboard score with no findings listed. A score shows nothing was fixed; the auditor needs the findings and their tickets.
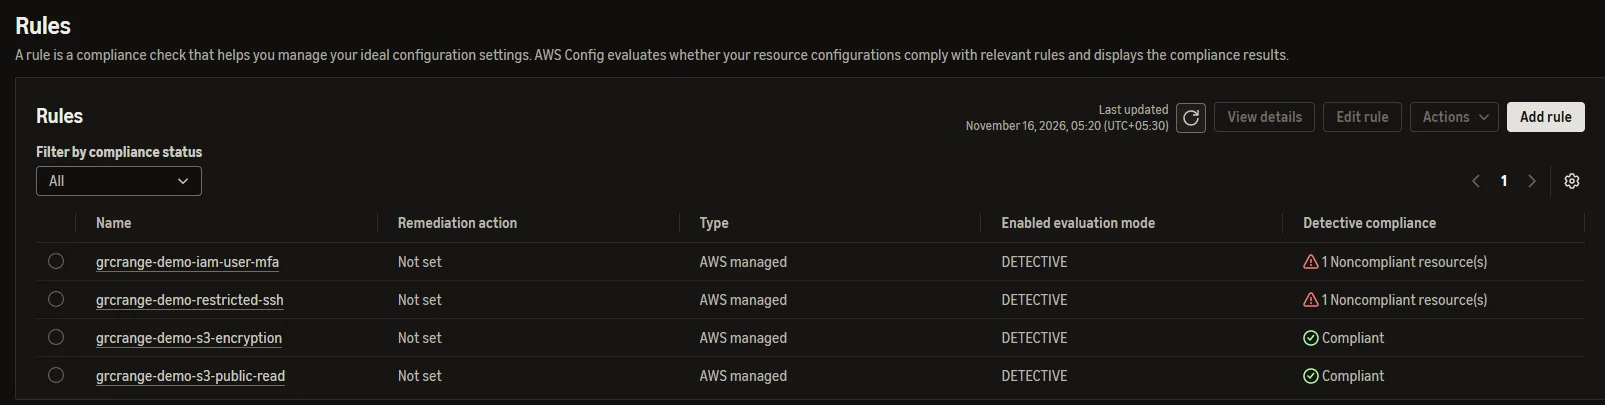
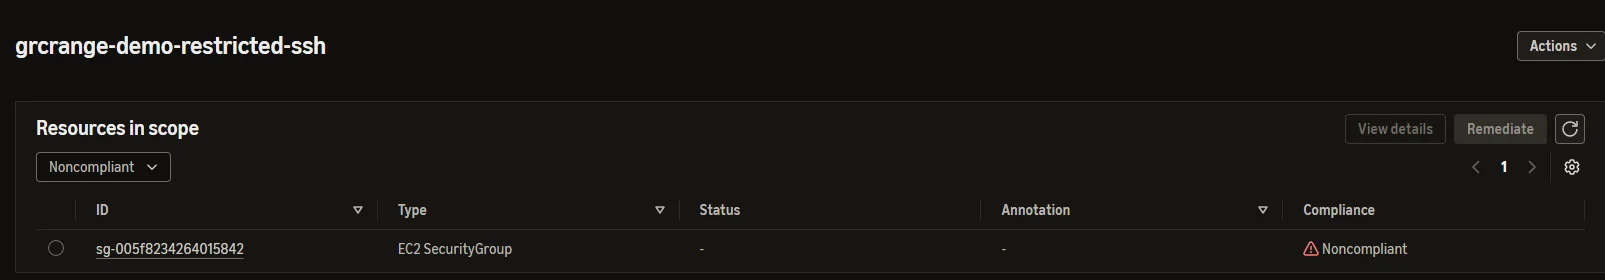
// FROM A REAL ACCOUNTAWS console, AWS Config · identifiers blurred
Defender for Cloud recommendations with ownersMicrosoft Defender for Cloud · proves CC7.1, A.8.8, A.8.9
Microsoft Defender for CloudSAMPLE
Defender for Cloud › Recommendations
Recommendations: High severity
| Recommendation | Severity | Resources | Status2 | Owner | Due date3 |
|---|---|---|---|---|---|
| Storage accounts should restrict network access | High | 1 of 6 | Completed | maria.s | 2026-09-15 |
| Machines should have vulnerability findings resolved | High | 2 of 14 | In progress | david.e | 2026-10-10 |
- 1Export date and subscription.
- 2Status shows progress, not just detection.
- 3Owner and due date make it a managed control.
Weak version: No owners or dates. Findings with no one responsible are just a list.
// REMEMBER THIS
Found, rated, owned, fixed on time. That is vulnerability management.
// CHECK YOURSELF
1. What does CVSS measure?
2. Which finds flaws in how an application's logic works?
3. The policy says critical fixes in 7 days. One took 19. That is...