What a log line is
A log is a record of an event. A good log line answers five questions:
| Who | What | When | Where | Result |
|---|---|---|---|---|
| maria.s | changed a firewall rule | 2026-10-01 18:03 | production account | success |
Kinds of logs you will meet
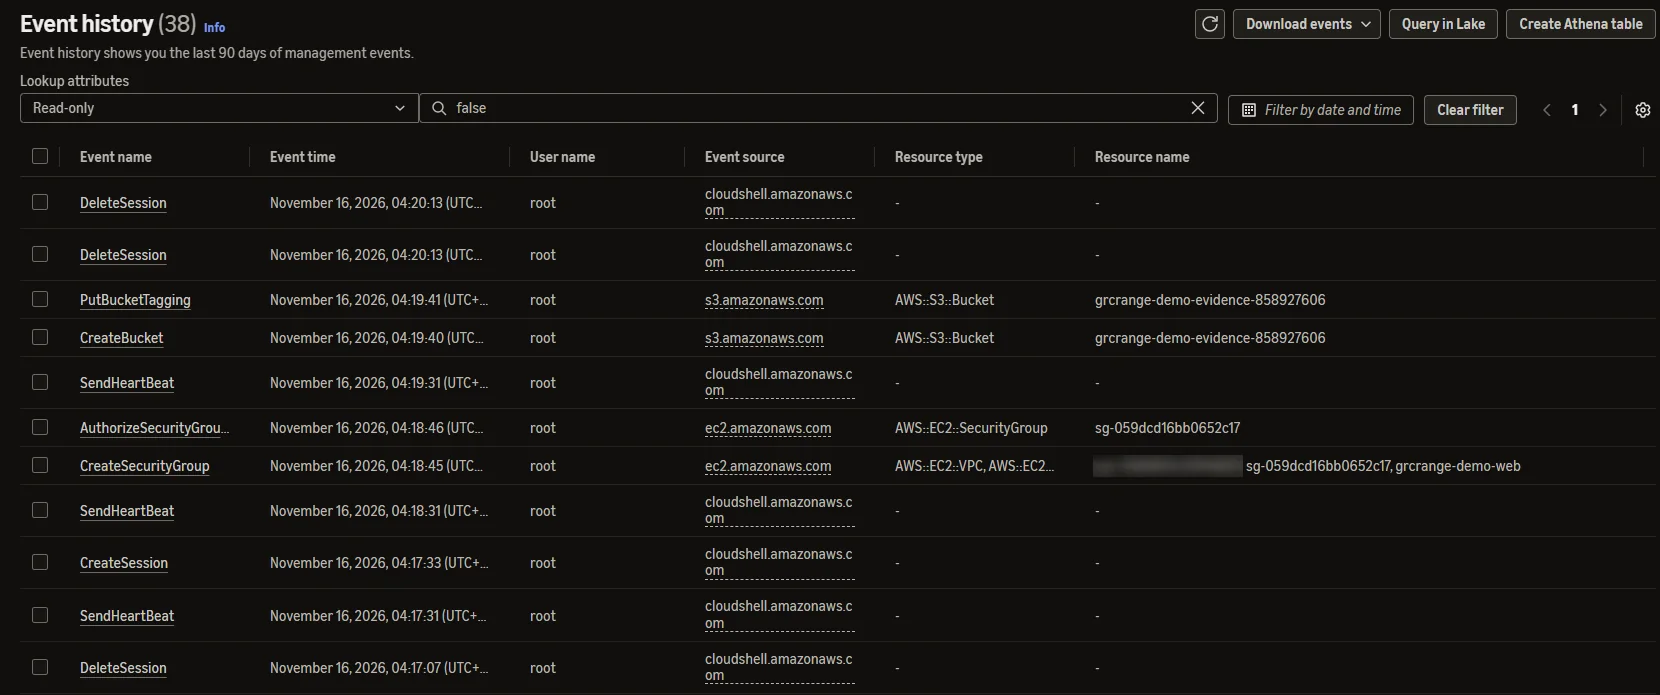
- Audit logs from the cloud: AWS CloudTrail, Azure activity logs, Google Cloud Audit Logs. They record admin actions.
- Sign-in logs from the identity provider: who logged in, from where, with MFA or not.
- Application logs from the company's own software.
Logging is not monitoring
Logging means the record exists. Monitoring means something reads it and raises an alert when something looks wrong, such as a login from an unusual country. A SIEM collects logs from many systems and runs those rules. Alerts are only useful if someone triages them, deciding whether each one is an incident.
Three things auditors check
- Coverage: is logging on everywhere in scope, in every account and region?
- Protection and retention: can admins delete logs? How long are they kept?
- Response: show an alert from the period, and what someone did about it.
Time matters
If system clocks disagree, logs cannot be lined up during an investigation. That is why clock synchronisation is a control (ISO A.8.17).
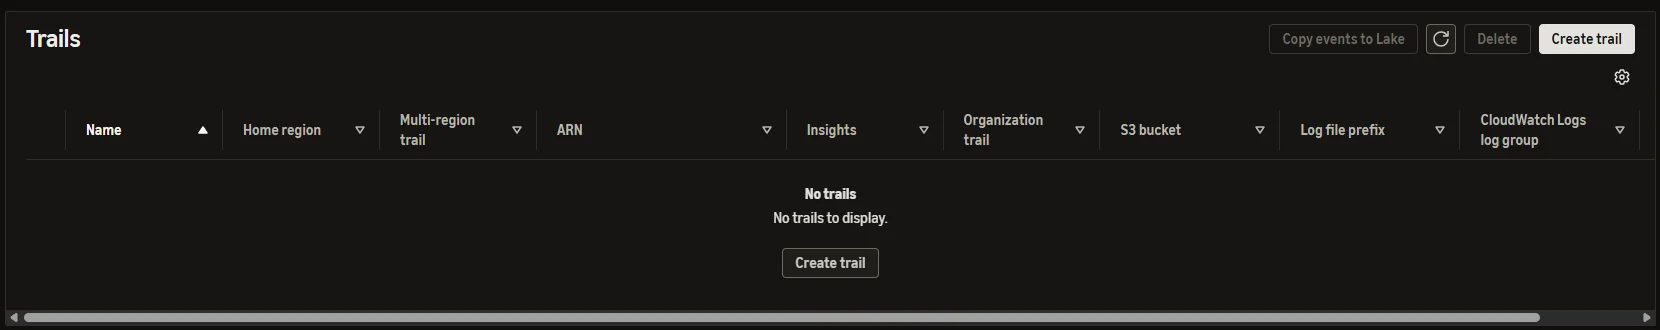
org-audit-trail
- LoggingOn2
- Multi-region trailYes3
- Apply trail to my organizationEnabled for all accounts
- Log file validationEnabled4
- S3 bucketcomplyoo-audit-logs (Object Lock: Compliance, 400 days)
- Management eventsRead and write
- 1Date of capture. For a Type II, take this more than once across the period, or show it was never turned off.
- 2Logging is on. This is the control itself.
- 3Multi-region. A single-region trail leaves gaps attackers use.
- 4Log file validation and Object Lock show the logs are protected from tampering.
Weak version: Single region, in one account only. The auditor will ask about every other region and account, and logging gaps there are a finding.
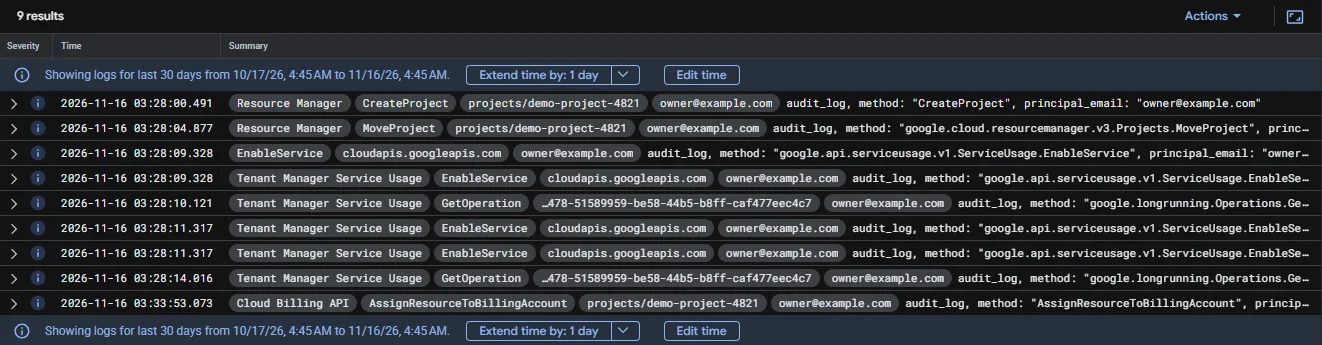
Admin Activity audit logs
| Timestamp | Principal2 | Method | Resource |
|---|---|---|---|
| 2026-10-02 22:41:07 | deploy@complyoo-prod.iam | run.services.replaceService | api |
| 2026-10-02 18:03:55 | maria.s@complyoo.com | SetIamPolicy | complyoo-prod3 |
| 2026-10-01 09:12:40 | david.e@complyoo.com | compute.firewalls.patch | allow-lb |
- 1Query date and project.
- 2Each entry names a person or service account.
- 3An IAM policy change, exactly the kind of event an auditor traces back to an approved request.
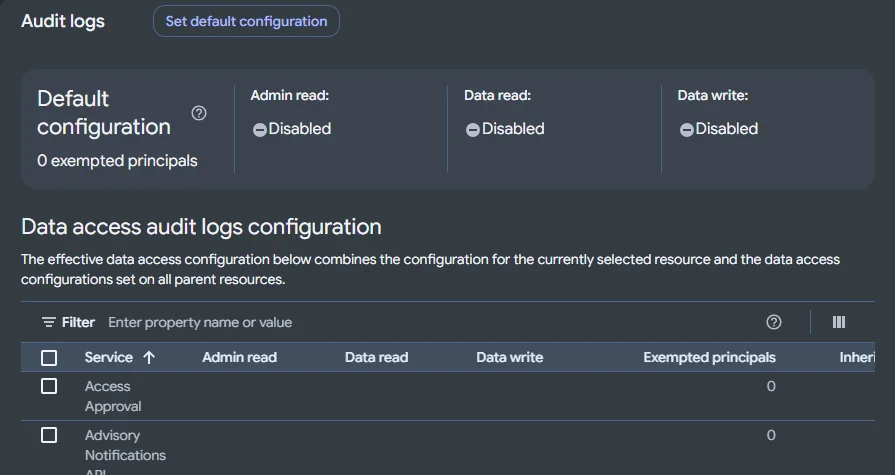
Weak version: A screenshot of the logging settings page only. It shows logging exists, not that anyone reviews what it records.
Logging records. Monitoring notices. You need both.
1. Logging is on, but alerts go to a mailbox nobody reads. Which part fails?
2. Which of these is a cloud audit log?
3. Why do auditors care whether admins can delete logs?