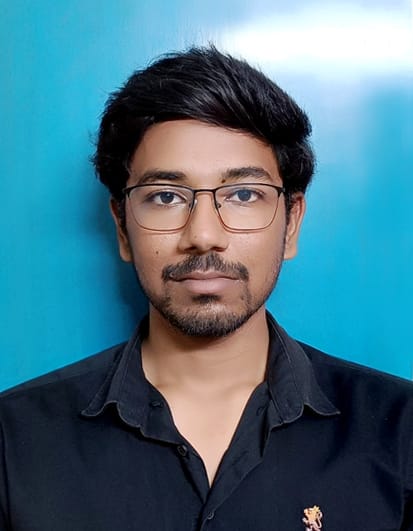
T Yashwanth Raj
Computer Science graduate
I am a Computer Science graduate with hands-on training and lab experience in cybersecurity, security monitoring, SIEM, EDR/XDR, alert triage, log analysis, threat detection, and incident investigation. I designed a rule set to bucket simulated security events into low/medium/high priority using log evidence alone, aimed at cutting analyst time spent on noise and surfacing the handful of events that actually mattered. My current focus is on applying my technical knowledge in a real-world security environment.
Skills
Projects
SIEM Alert Triage Simulation
Designed a rule set to bucket simulated security events into low/medium/high priority using log evidence alone, aimed at cutting analyst time spent on noise and surfacing the handful of events that actually mattered.
Phishing Email Forensics
Broke down suspicious emails at the header, domain, and payload level — sender spoofing, lookalike domains, malicious attachments — and turned the findings into a repeatable triage checklist.
Windows Event Log Investigation
Worked through Windows Security event data to isolate failed logons, lockout patterns, and privileged-account activity, mapping how that evidence supports a real incident narrative.
Network Traffic Fundamentals for Detection
Studied TCP, UDP, DNS, DHCP, and ARP behavior specifically to build a 'what does normal look like' baseline, then used that baseline to spot deviations worth flagging.
Threat Intel IOC Correlation
Cross-referenced sample IPs, domains, and file hashes against log data to practice deciding, with limited context, whether an indicator needs escalation or just monitoring.
Education
Keshav Memorial Institute of Technology
Bachelor of Computer Science • 2021-2025
7.3
Sri Chaitanya Junior Kalasala
Intermediate • 2019-2021
90.4
DAV Public School
SSC • 2019
91.2
Get in Touch
Interested in collaboration or just want to say hello? Feel free to reach out!