Rishav Soni
Entry-level SOC Analyst
I am an entry-level SOC Analyst with hands-on exposure to SIEM tools, log analysis, and security monitoring through virtual labs. I have participated in threat analysis and hands-on security labs. My current focus is on contributing to blue team operations and enhancing defensive security skills.
Skills
Projects
SOC Analyst Virtual Labs
Monitored simulated security alerts using Splunk SIEM. Investigated phishing scenarios and mapped attacker behavior to MITRE ATT&CK. Performed packet analysis using Wireshark to identify suspicious network traffic.
Experience
Cybersecurity Centre of Excellence (CCoE), UEM Kolkata
Participated in threat analysis, hands-on security labs, and blockchain fundamentals, cryptographic principles in blockchain, hashing in blockchain, digital signature, hands-on practical sessions.
Future interns
April 2026 - May 2026
Assisted in SIEM monitoring, log analysis, vulnerability assessment, and incident analysis.
Certifications
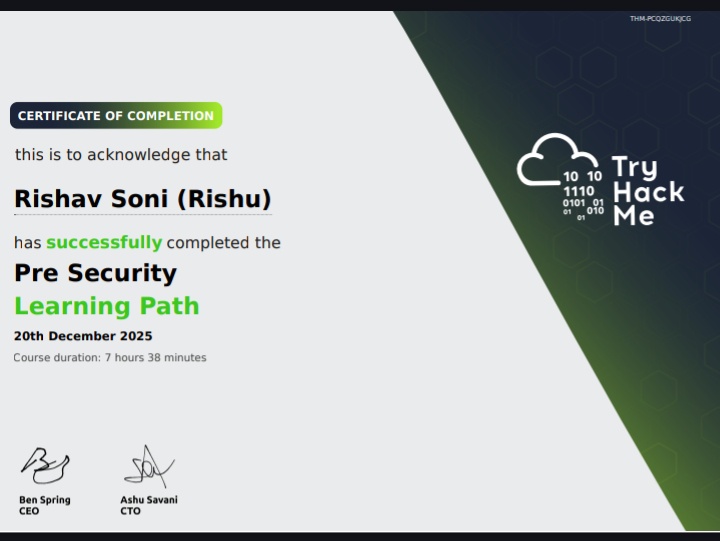
Tryhackme - pre security learning path
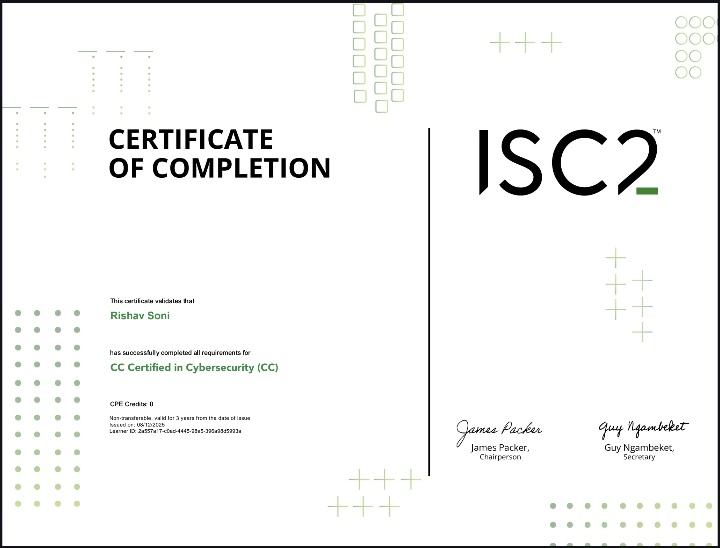
ISC2 Certified in Cybersecurity (CC)
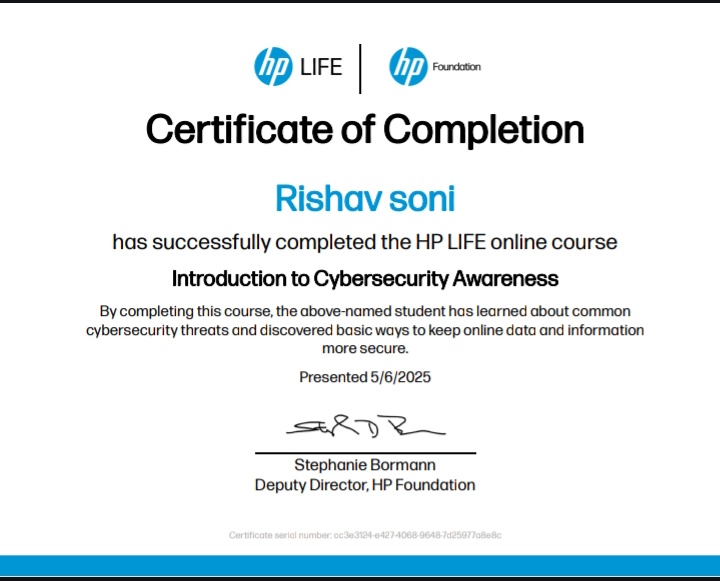
Cybersecurity Awareness
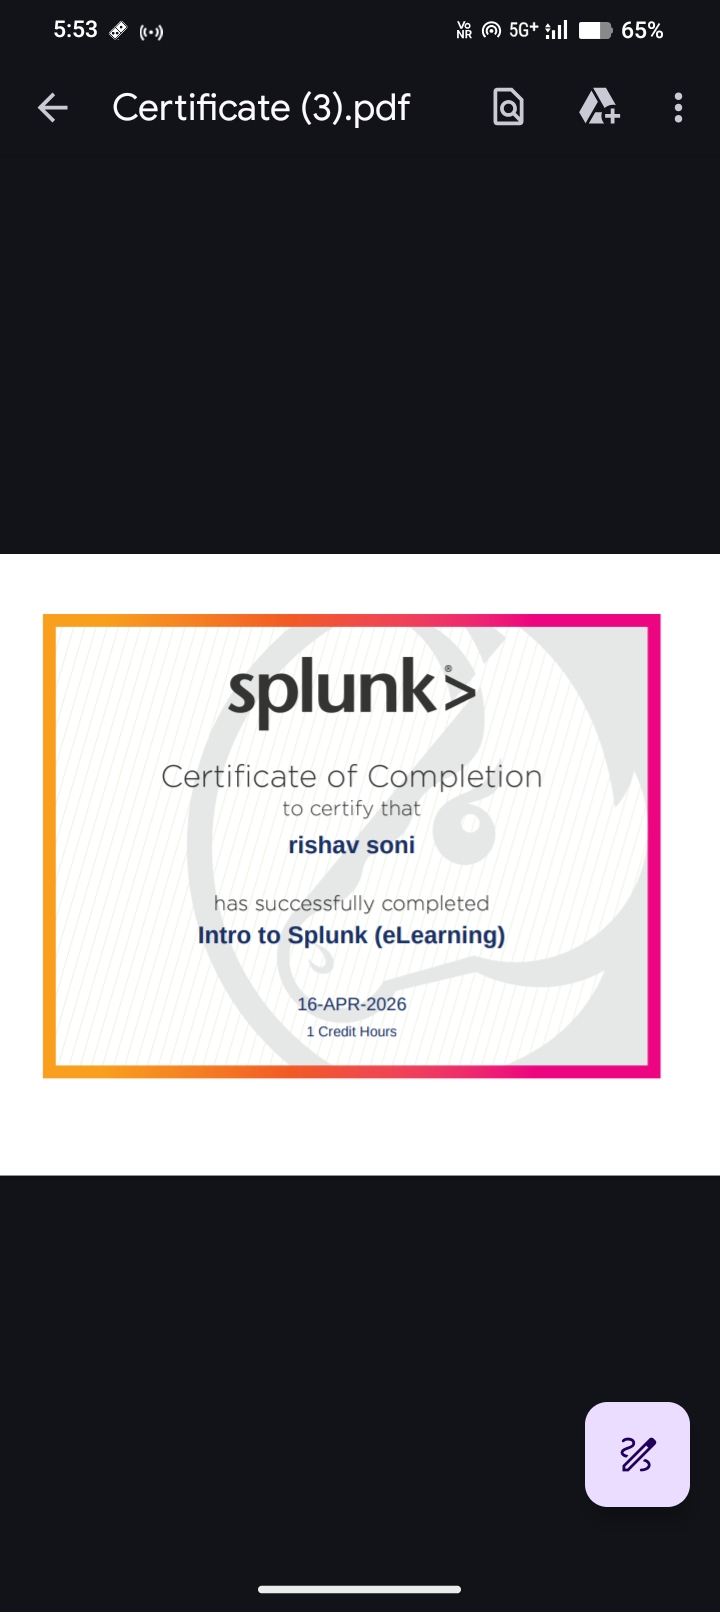
Intro to Splunk
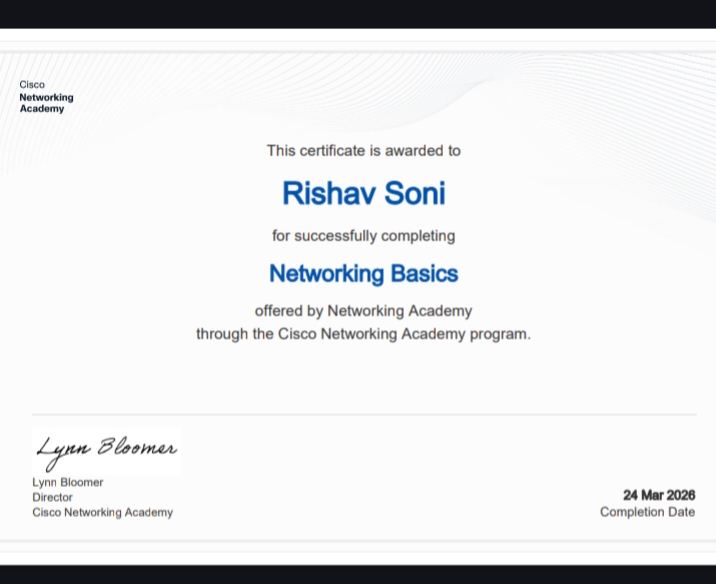
CISCO - Networking Basics
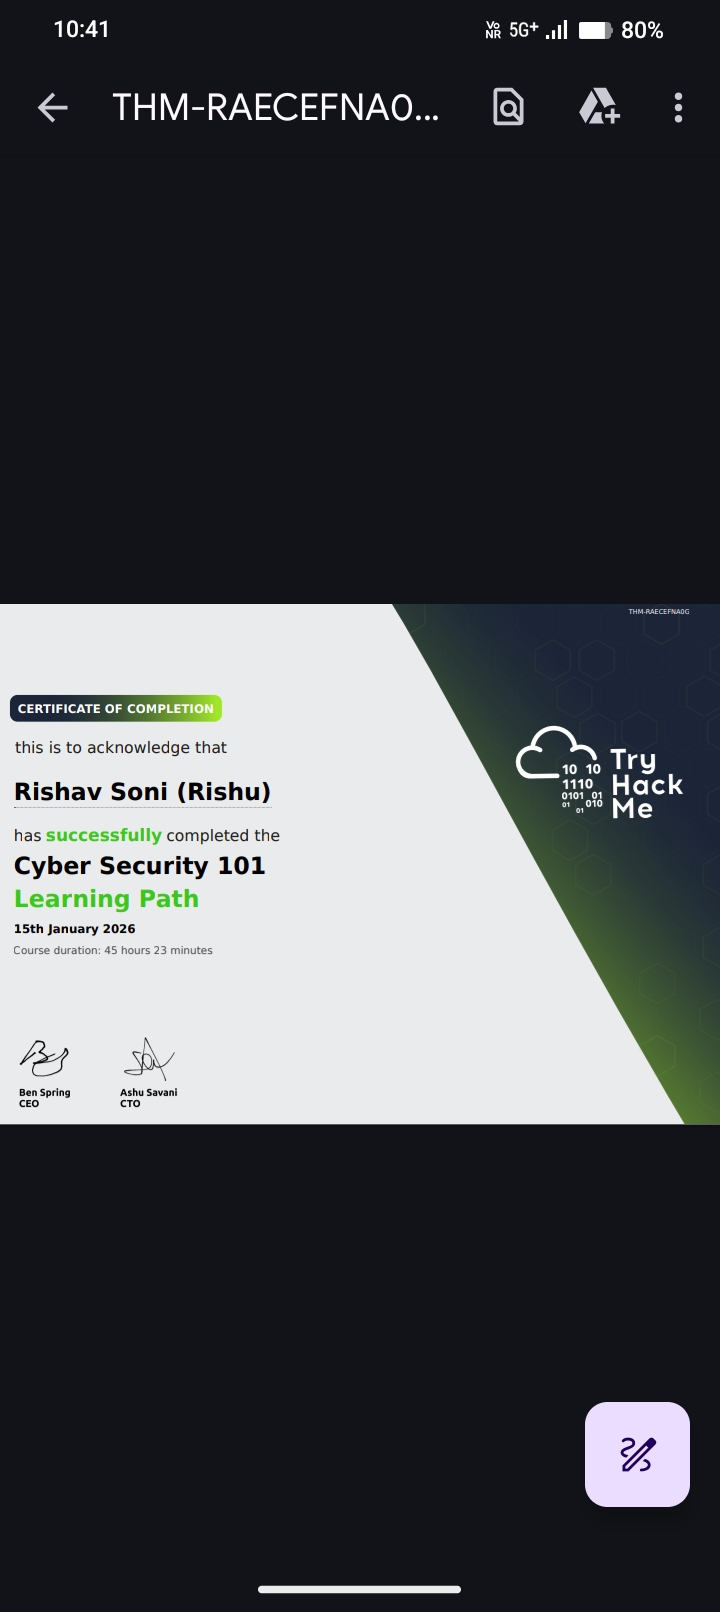
Tryhackme - cybersecurity 101 learning path
Education
Birla Institute of Technology, Mesra
Bachelor of Computer Application • 2023-2026
7.95
Get in Touch
Interested in collaboration or just want to say hello? Feel free to reach out!